Facts from Stripe's documentation, read on 28 October 2026. Stripe updates its MCP server often. Check its pages before you rely on any detail.
The Stripe MCP server lets an AI assistant work with your Stripe account through one remote address, mcp.stripe.com. Stripe labels it a public preview. It can read almost any Stripe object. It can also write: create refunds, cancel subscriptions, void invoices. What your agent can actually do depends on the permissions you give it, and Stripe gives you the tools to limit them.
What the Stripe MCP Server Is
MCP, the Model Context Protocol, is how AI assistants connect to outside tools. Stripe runs its own MCP server, so an assistant can call the Stripe API and search Stripe's documentation.
Stripe documents setup for Cursor, Claude, ChatGPT, Codex and VS Code, and any other client that supports MCP can use the same address. There are two ways to sign in.
OAuth is for an assistant acting as you. The client opens Stripe's consent page, and you choose which live accounts or sandboxes it can reach, with different permissions for each.
Agent API keys are for software that needs its own, lasting access. An agent API key is a restricted API key tagged for an AI agent when you create it.
What It Can Read
Most of the server's reach goes through two general tools. One, stripe_api_read, reads data "with any Stripe API GET method". Customers, charges, refunds, invoices, subscriptions, payouts and balance transactions are all on Stripe's list of supported methods.
There are also specific tools, including account information, documentation search, an integration planner and, in preview, stripe_analytics for metrics and reports. For a reporting question, reading is all an assistant needs.
What It Can Write
The second general tool, stripe_api_write, writes "with any Stripe API POST, PATCH, PUT and DELETE method". Stripe's list of supported methods shows how far that reaches. The table below is a selection from that list.
Resource | What the server can do |
|---|---|
Refunds | Create a refund |
Subscriptions | Create, update or cancel |
Invoices | Create, update, finalize, void, or mark uncollectible |
Customers | Create or update |
Coupons and promotion codes | Create coupons and codes; update or delete coupons |
Products and prices | Create or update |
Payment links and Checkout Sessions | Create; update payment links |
Disputes | Update |
Webhook endpoints and event destinations | Create; update event destinations |
Tax | Update settings; create or update registrations |
Treasury adds tools in public preview, including send_money and transfer_money, which move funds.
Stripe puts one check in place itself. When an agent connects with your own sign-in, Stripe requires human confirmation before "certain stripe_api_write actions, such as refunds and outbound payments". You approve the request at a link the agent gives you. An approval not given within 24 hours expires.
The 30 November 2026 Key Change
If your agent connects with an API key, this date matters. Stripe's notice is direct: "Starting in December, Stripe MCP will stop accepting full-access secret keys and restricted API keys without the Agent tag."
From December, an API-key connection needs an agent API key, or you reconnect with OAuth. A request with any other key gets a 401 error.
The change brings a safeguard with it. Agent-tagged keys are subject to approval rules, which need a designated reviewer to approve a sensitive action before it runs. Stripe's approvals page lists six default rules for agent keys: a refund being created, a subscription being canceled, an outbound payment or outbound transfer being initiated, a payout being created, and a currency conversion being created. You can change their conditions or reviewers, or delete them. You can add rules for other actions, such as creating a payment intent, and set conditions on amount or rate. A request nobody approves within 14 days expires.
These rules govern what an agent may write. They do not make it read-only.
How to Keep a Stripe Agent Read-Only
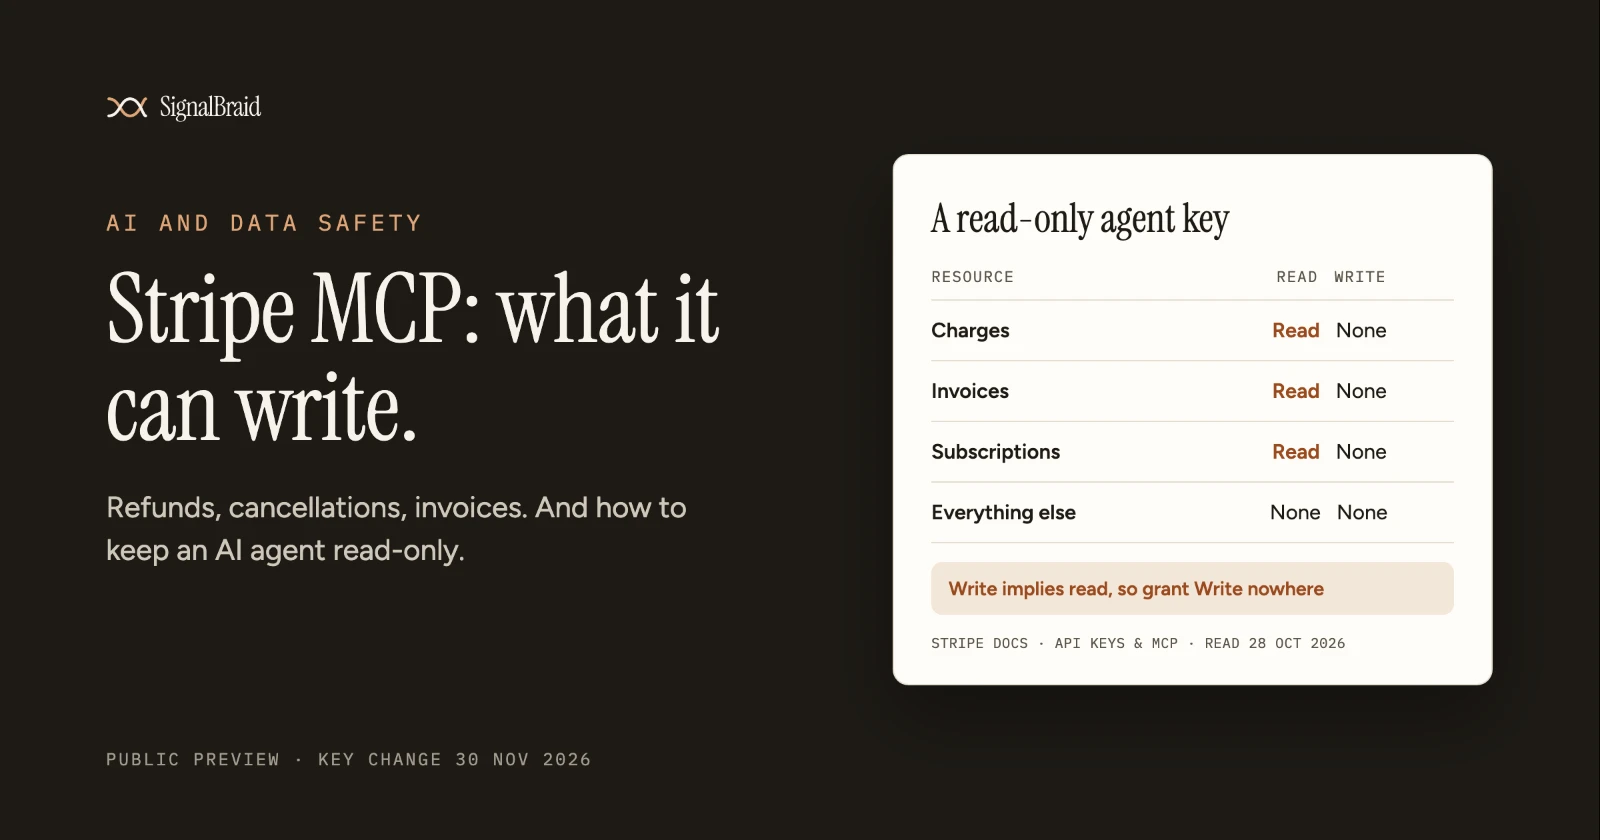
The firmest limit is the key itself. Every restricted key, agent keys included, has a permission for each resource: None, Read or Write.
"Write permissions imply read permissions", so a key that should only read must hold no Write permission anywhere.
- Create an agent API key in a sandbox first. Choose "Authorizing agent access to your account" when Stripe asks how the key will be used.
- Set Read only on the resources your questions need, such as Charges, Invoices and Subscriptions. Leave everything else at None, which is the default.
- Test it. Ask the assistant your usual questions. If a request needs a permission the key lacks, Stripe refuses it with an error that names the missing permission.
- Repeat in live mode with the same permissions, and store the key as Stripe advises: in a secrets vault, or an environment variable if your platform doesn't have one.
- Keep tool approval on in your AI client. Stripe recommends it so you can "review tool calls before they run".
Two Dashboard settings help a team. An administrator can turn MCP access on or off for everyone, separately for live mode and sandboxes. And every OAuth connection appears under OAuth sessions, where you can revoke it.
Where Read-Only Has Limits
Stripe's documentation lists the same tools for every connection. With a read-only key, Stripe refuses a write rather than hiding the tool, so the assistant can still try. The limit holds, but expect the occasional refused request.
Stripe does not say whether OAuth consent can be limited to reading. If you need a firm read-only connection, use a key whose permissions you set yourself.
Reading is still access. A key that can read customers sees names and email addresses. Grant Read only on what your questions need.
Stripe also warns about prompt injection, where text in the data an assistant reads tries to steer it. Its advice is caution when the Stripe server runs beside other MCP servers.
Users want more. A GitHub discussion in Stripe's AI repository, opened in January 2026, asks for caps such as a maximum number of refunds per day. At the time of writing, its replies come from other users.
What SignalBraid Does Today
SignalBraid is in development, with access by invitation.
Its AI connection is designed to be read-only: it is designed to have no tool that writes, and to keep your Stripe credentials away from the AI. A Stripe connection is planned, not available yet.
Status on 28 October 2026, from the registry: Stripe: Planned. MCP (AI connection): Planned, read-only.
Stripe pages last verified: 28 October 2026
Sources (read 28 October 2026)
- Stripe Docs, "Model Context Protocol (MCP)". https://docs.stripe.com/mcp
- Stripe Docs, "API keys" (section "API keys for autonomous agents"). https://docs.stripe.com/keys
- Stripe Docs, "Restricted API keys". https://docs.stripe.com/keys/restricted-api-keys
- Stripe Docs, "Set up two-party approvals". https://docs.stripe.com/account/approvals
- GitHub, stripe/ai Discussion #216, "Add MCP server actions limits" (opened 15 January 2026). https://github.com/stripe/ai/discussions/216
- SignalBraid connector and output registry, as rendered on signalbraid.com on 28 October 2026.